

Key takeaways
• Non-functional requirements decide whether your product survives day two. Features get a user to sign up. NFRs — performance, security, scalability, reliability — decide whether they stay, recommend you, and pass procurement.
• Use ISO/IEC 25010:2023 as your spine. Nine quality characteristics (functional suitability, performance efficiency, compatibility, interaction capability, reliability, security, maintainability, flexibility and the newly added safety) are the canonical NFR taxonomy. Map every requirement to one of them.
• Every NFR must be measurable, testable, and owned. “Fast” and “secure” are not requirements. “p95 API latency <500 ms under 1,000 concurrent users, verified by k6 nightly” is.
• Over-spec costs money you don’t have. Moving from 99.9% to 99.99% uptime can multiply infrastructure cost 5–10×. Spec for the next 12 months, not the dream pitch deck.
• Bake compliance in, don’t bolt it on. GDPR, HIPAA, PCI DSS v4.0.1, SOC 2, the EU AI Act and, since 11 September 2026, the EU Cyber Resilience Act reporting duties all imply specific NFRs (encryption, audit logs, RTO/RPO, data residency, 24-hour vulnerability reporting). Adding them after launch is a rewrite, not a feature.
Updated October 2026: EU Cyber Resilience Act reporting (live since 11 September 2026), the final AI Act Digital Omnibus dates, HIPAA Security Rule status, and a quick answer to what NFR means.
Why Fora Soft wrote this playbook
Fora Soft is a software development company that has been shipping video, AI and real-time products since 2005 — 250+ delivered software products across telemedicine, e-learning, video surveillance, live streaming and B2B SaaS. Most of those products had a moment when an analyst, a CTO or a buyer pulled out a non-functional requirements document and decided whether we were the right partner. We’ve seen what works and what gets a vendor cut on slide 3.
This playbook condenses what we use internally for products like BrainCert (large-scale e-learning with strict uptime SLAs), TransLinguist (real-time video interpretation, sub-300 ms latency targets), MyOnCallDoc (HIPAA-grade telemedicine) and Sprii (live video shopping, peak-traffic spikes). It’s written for the person who has to brief a development partner — product owner, head of product, founding engineer, procurement — not for academic completeness. When a client wants this done before the first sprint, our software product planning and analytics team writes the NFR section together with the scope and roadmap, so every threshold has a budget behind it.
If you’re hiring a partner now, the fastest way to test their NFR maturity is the conversation, not the proposal. Below is the structure we use to lead it.
Need a sanity check on your NFR list before signing a vendor?
30 minutes with a Fora Soft architect — we’ll tell you what’s missing, what’s over-spec, and what will blow up your infra bill.
What is a non-functional requirement, in one paragraph
A non-functional requirement (NFR) describes how well a system must do its job, not what it does. Functional requirements describe behaviour (“The user can publish a post”). NFRs describe quality attributes around that behaviour (“Publishing a post completes within 800 ms p95, survives a single-AZ outage, and stores the post encrypted at rest”). NFRs are also called quality requirements, technical user stories or, in the ISO/IEC 25010:2023 vocabulary, quality characteristics.
A useful mental model: a functional requirement is the verb. A non-functional requirement is every adverb you’d ever attach to that verb — quickly, securely, reliably, accessibly, cheaply, in any time zone, on any device. Without those adverbs, “the user can log in” is true even if logging in takes 14 seconds, leaks the password, and only works in Chrome.
NFR meaning: what the acronym stands for in IT
In software and IT, NFR stands for non-functional requirement: a requirement that sets how well a system must work (speed, availability, security, accessibility, cost) rather than which feature it provides. “NFR requirements” is a common doubling of the same term.
Outside engineering the acronym means other things. In software licensing, NFR means “not for resale” (copies vendors give partners and reviewers), and in the US it is also the National Finals Rodeo. In a spec, a backlog, a test plan or a security review, NFR always means non-functional requirement.
Three phrases people search for, answered in one line each:
- NFR in cybersecurity means the security requirements of a system written as measurable rules: encryption, MFA, patch deadlines, audit-log retention and vulnerability reporting. Under the EU Cyber Resilience Act, manufacturers must send an early warning about an actively exploited vulnerability within 24 hours from 11 September 2026 (European Commission, 2026).
- NFR environment (also NFT or performance environment) is a production-like environment where non-functional tests run: load, soak, failover drills and security scans. It needs production-sized data and infrastructure, or the numbers it produces mean little.
- NFR in requirements models: in FURPS+, the F is functionality and URPS (usability, reliability, performance, supportability) plus the “+” constraints are the non-functional part. ISO/IEC 25010:2023, covered below, is the standard taxonomy today.
NFR vs functional requirement — the side-by-side
Most teams confuse the two because their backlog tools force everything into the same template. Here’s the difference put bluntly.
| Dimension | Functional requirement | Non-functional requirement |
|---|---|---|
| Answers | What does the system do? | How well does it do it? |
| Granularity | Per feature / user story | System-wide or per critical path |
| Verification | Acceptance test — does it happen? | Measurement — latency, uptime, audit, scan |
| When it fails | Feature missing / broken | Slow, unsafe, unstable, unscalable, non-compliant |
| Cheap to fix later? | Often yes | Almost never — usually requires re-architecture |
| Example | “Doctor can start a video visit” | “Visit starts in <3 s, runs over E2EE, HIPAA-logged, 99.95% available” |
The last row is the one buyers under-weight. Adding a feature is a sprint. Adding HIPAA-grade audit logging or pulling latency from 4 s down to 800 ms after launch is usually a rewrite of the data layer or the transport.
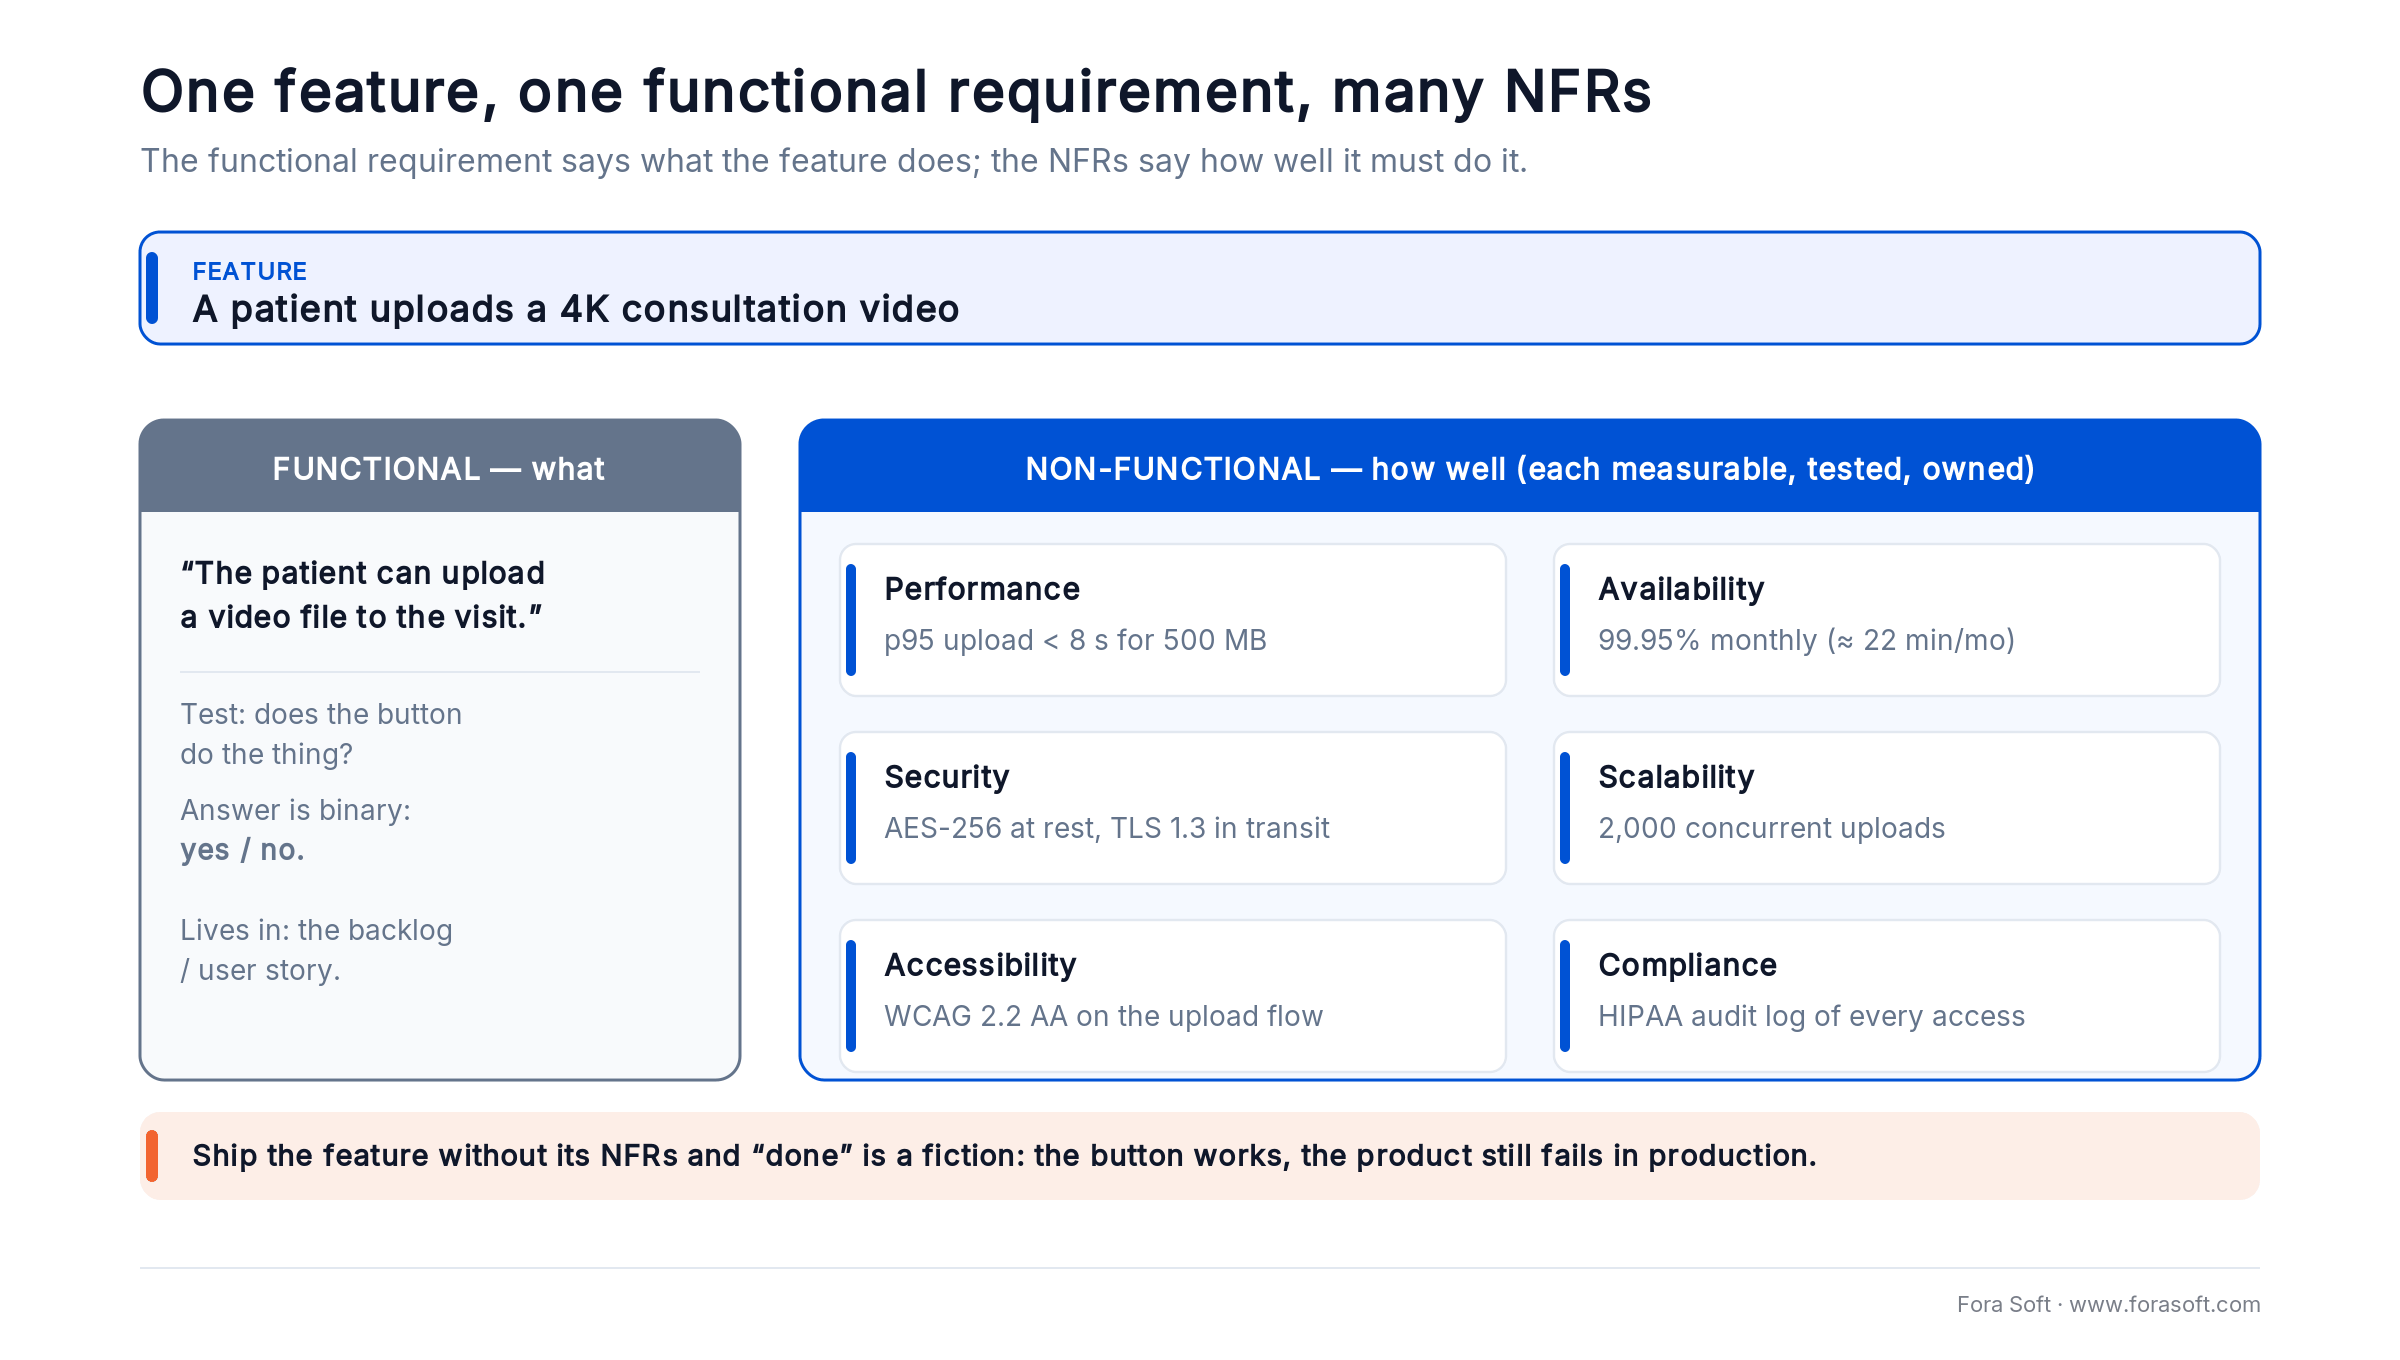
Figure 1. A functional requirement describes one behaviour; its non-functional requirements describe how well it must run — each measurable, tested and owned.
The ISO/IEC 25010:2023 spine — nine characteristics every NFR maps to
ISO/IEC 25010 is the international standard for software product quality. The 2023 revision moved from eight top-level characteristics to nine: it added safety as a top-level characteristic and renamed usability to interaction capability and portability to flexibility (most articles online still cite the old eight from the 2011 model). So if you are asked which ISO standard covers non-functional requirements: ISO/IEC 25010:2023 defines what quality means, and ISO/IEC/IEEE 29148 covers how requirements, NFRs included, are written and managed. Use the nine as the table of contents for your NFR document — if a stakeholder requests a requirement that doesn’t map to any of them, it’s probably not an NFR. For a copy-paste checklist with worked examples in each category, see our non-functional requirements checklist.
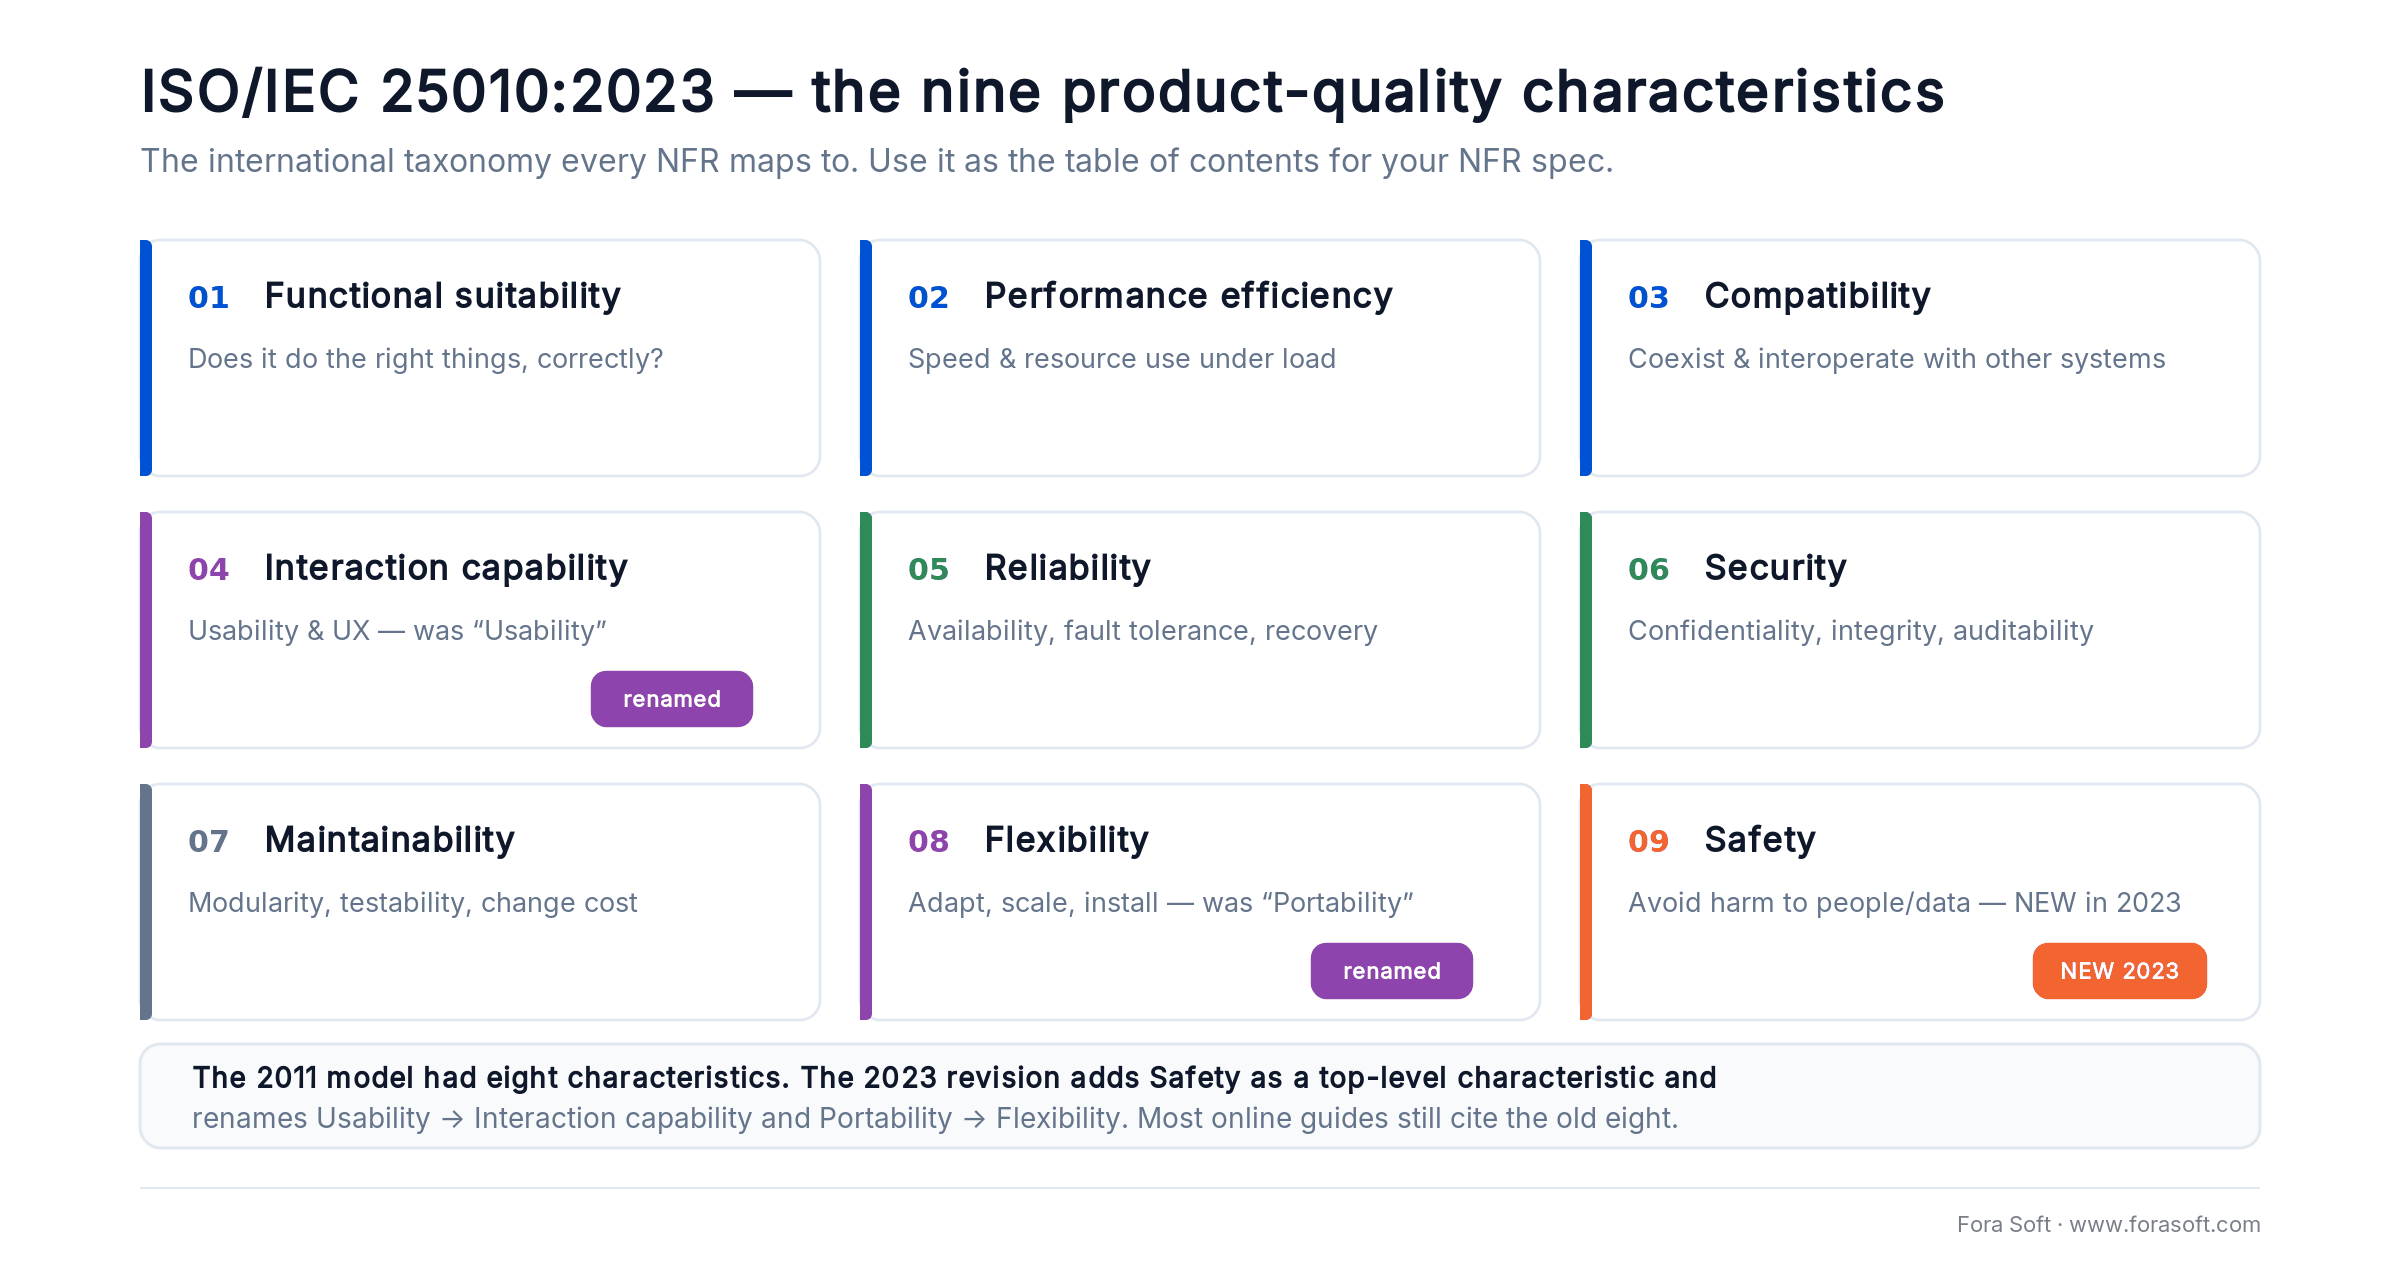
Figure 2. ISO/IEC 25010:2023 defines nine product-quality characteristics. The 2011 model had eight — safety is new, and usability and portability were renamed.
1. Functional suitability
Completeness, correctness, appropriateness. The bridge between functional and non-functional. Example: “The platform shall support every workflow listed in section 2.1 with zero P1 defects in production.”
2. Performance efficiency
Time behaviour (latency, throughput), resource use (CPU, memory, bandwidth), capacity (max concurrent users, max data volume). Express in percentiles, not averages: p50/p95/p99. Averages hide the bad afternoons.
3. Compatibility
Co-existence with other systems on the same infrastructure, and interoperability through documented APIs and data contracts (OpenAPI 3.2, released September 2025 per the OpenAPI Initiative, AsyncAPI, gRPC, webhooks).
4. Interaction capability (was “Usability”)
Learnability, operability, accessibility (WCAG 2.2 AA is now the default and, since October 2025, also the international standard ISO/IEC 40500:2025; the EAA has been mandatory in the EU since 28 June 2025), user error protection, user engagement, inclusivity and user assistance. Yes, accessibility is an NFR. No, “intuitive UI” is not.
5. Reliability
Maturity (low defect rate), availability (uptime%), fault tolerance (graceful degradation), recoverability (RTO/RPO). The hardest characteristic to fake under audit and the easiest to over-promise on a sales call.
6. Security
Confidentiality (encryption, RBAC), integrity (input validation, signed events), non-repudiation (immutable audit logs), accountability, authenticity (MFA, device binding). This is also where most compliance frameworks bite.
7. Maintainability
Modularity, reusability, analysability, modifiability, testability. The NFR your CFO will care about three years in. Good maintainability spec keeps the second team productive.
8. Flexibility (was “Portability”)
Adaptability across environments, scalability (added as a sub-characteristic in the 2023 revision, which is where ISO now files scalability NFRs), installability, replaceability. Express as deployment targets (containers, K8s, specific cloud regions) and exit guarantees (data export, infra-as-code parity).
9. Safety (new in 2023)
Freedom from unacceptable risk to people, property or the environment — the characteristic ISO/IEC 25010:2023 added at the top level. It covers operational constraint (the system stays within safe limits), fail-safe behaviour, hazard warning and safe integration. It matters most for health, automotive, industrial and any AI that can act on the physical world. Example: “On loss of the vitals feed, the monitor raises an audible alarm within 2 s and fails to the last-known-good reading, never to a blank screen.”
The 12 NFR categories that actually appear in real specs
ISO is the spine; this is the body. In production specs we hand to engineering, NFRs collapse to twelve working categories. Each one needs a metric, a threshold, an owner, and a verification method. This section is the definitional tour; if you want the ready-to-use version — a 14-category checklist with concrete examples and a copy-paste NFR template — use our non-functional requirements checklist and examples.
Performance & latency
p50, p95, p99 latencies for every critical path. Web pages: 1 s p95, 2.5 s p99 is the modern bar (Largest Contentful Paint <2.5 s is Google’s Core Web Vitals threshold, and responsiveness is measured as Interaction to Next Paint ≤200 ms, the metric that replaced First Input Delay in March 2024). API calls: <500 ms p95 for B2B SaaS, <100 ms for high-frequency endpoints. Real-time video: <300 ms glass-to-glass for conferencing, <500 ms for live commerce.
Scalability
Concurrent users at peak, peak-to-average ratio, growth horizon (12–24 months), and the degradation curve (“at 10× load, p95 stays under 1.5 s”). “Supports 100k users” is meaningless without specifying load shape and degradation tolerance.
Availability & reliability
Uptime SLO, MTBF, MTTR, error budget. Pick a number you can defend with infrastructure spend (see the next section).
Recoverability (RTO & RPO)
RTO = how long until service is back. RPO = how much data loss is acceptable. Tested in real drills, not paper runbooks.
Security & privacy
Encryption (AES-256 at rest, TLS 1.3 in transit), MFA, RBAC, secret rotation, vulnerability SLAs, dependency-scan thresholds. See the Fora Soft WebRTC security primer for the real-time-comms angle.
Compliance
GDPR, HIPAA, PCI DSS v4.0.1, SOC 2 Type II, ISO 27001, FedRAMP, EU AI Act, EU Cyber Resilience Act, EU Data Act — pick the ones your market actually demands and translate them into concrete controls.
Usability & accessibility
WCAG 2.2 AA conformance, EAA compliance for EU, task-completion benchmarks, supported languages and locales, supported assistive technologies (VoiceOver, NVDA, TalkBack).
Compatibility
Browsers (named versions, the last two of Chrome, Safari, Firefox, Edge), OS (for example the current and previous major iOS release, Android 12+), device classes (low-end Android, iPad, desktop), screen sizes, integrations (specific CRMs, SSO providers, payment processors).
Maintainability & engineering quality
Test coverage thresholds (typically 70–85%), code review SLAs, doc freshness, dependency vulnerability SLAs, on-call rotation expectations, runbook coverage. A pre-takeover code audit is the cheapest insurance you’ll buy.
Observability
Metrics, logs, traces, dashboards, alerts. “p95 latency, error rate, saturation, traffic per service, all visible in <30 s, alert thresholds documented, on-call paged within 2 min of breach.”
Localization & geography
Languages, locales, time zones, currencies, data residency (EU data in Frankfurt, KSA data in Riyadh, etc.), CDN coverage, latency targets per region.
Cost & efficiency
Unit economics targets (cost per active user, cost per stream-minute, cost per stored GB), infra cost ceiling, autoscaling rules, idle-resource SLAs. Worked example for a video platform here.
Reach for explicit cost NFRs when: your unit economics will determine whether the product is viable at scale — e.g., live video, large-file storage, AI inference. Skip them only if compute is rounding error in your P&L.
The NFR matrix — metric, threshold, owner, test
Print this and put it next to your backlog. The thresholds in column 3 are reasonable defaults for a B2B SaaS — tune to your domain.
| Category | Metric | Default threshold | Owner | How you verify |
|---|---|---|---|---|
| Performance | API p95 latency | <500 ms at 1k RPS | Platform eng. | k6 / Gatling, nightly |
| Scalability | Concurrent users at peak | 10× current peak with <20% degradation | Architecture | Quarterly stress test |
| Availability | Monthly uptime | 99.9% (43 min/month) | SRE / DevOps | Synthetic monitoring + status page |
| Recoverability | RTO / RPO | RTO 4 h, RPO 15 min | Infra | Quarterly DR drill |
| Security | Encryption + vuln SLA | AES-256 at rest, TLS 1.3 in transit, P1 patch <48 h | Security | Pentest annually + SCA on every PR |
| Compliance | Framework certified | SOC 2 Type II within 12 mo | Legal + Sec | 3rd-party audit report |
| Usability | Accessibility conformance | WCAG 2.2 AA | UX / Eng. | axe + manual screen-reader pass |
| Maintainability | Test coverage / mean PR review | ≥80% lines; PR review <1 business day | Engineering | CI report; eng. metrics |
| Observability | MTTD / MTTA | Detect <2 min, ack <5 min | SRE | Incident retro |
| Cost | Cost per active user / minute | Defined & tracked monthly; no >15% MoM drift unflagged | FinOps | Cloud cost dashboards |
How to write a non-functional requirement that holds up in court (or procurement)
A good NFR has six fields. If any are missing, it’s a wish.
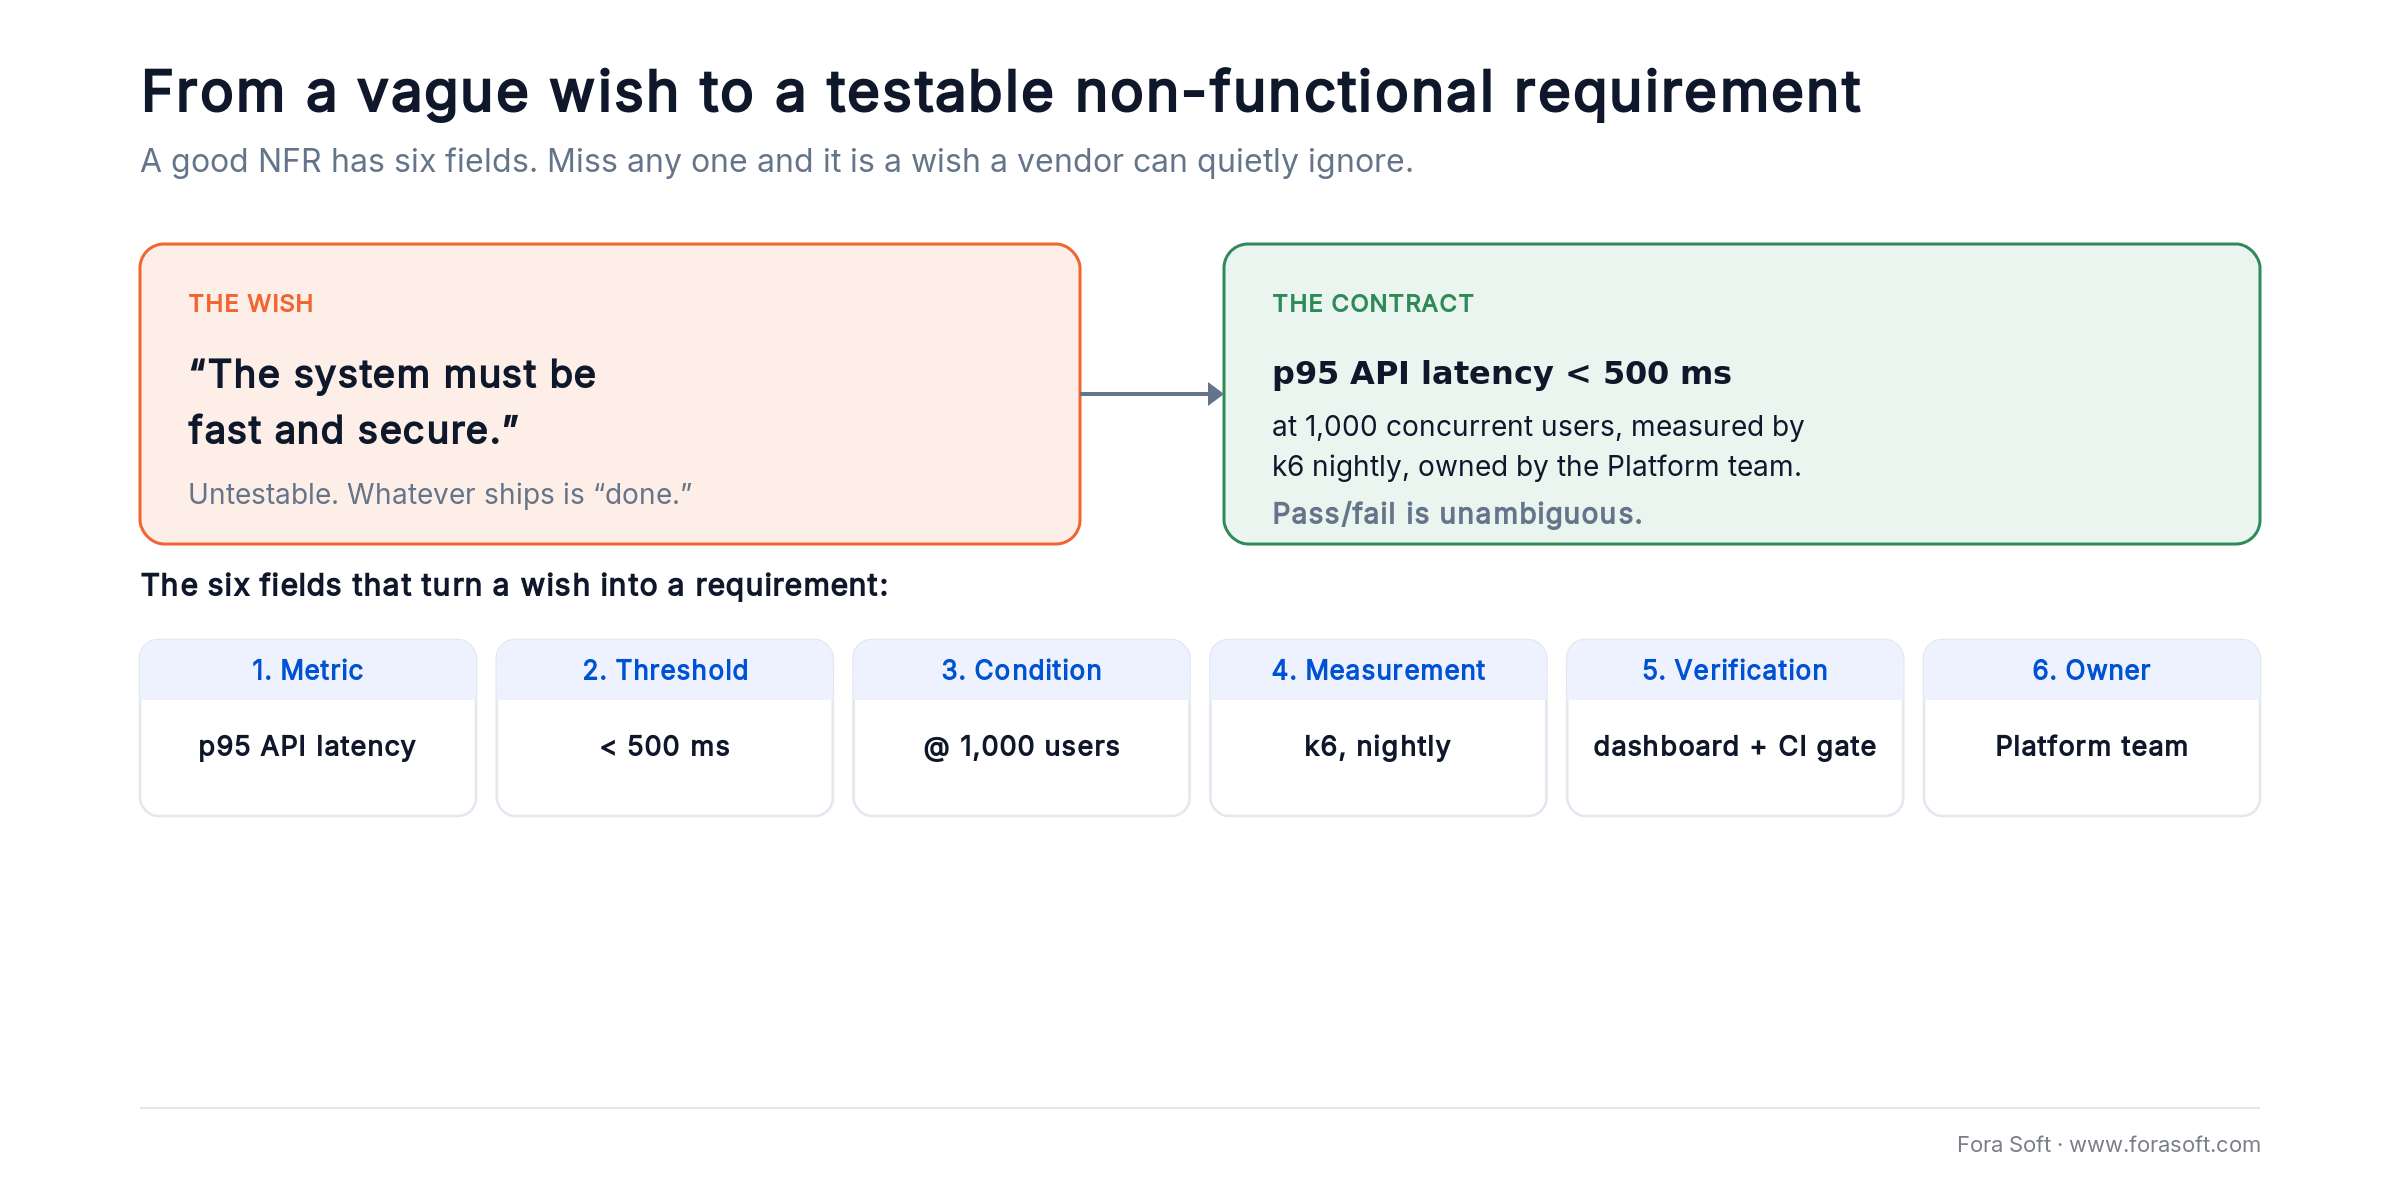
Figure 3. A good NFR has six fields. Fill all six and pass/fail is unambiguous; miss one and it is a wish a vendor can quietly ignore.
1. Subject. Which part of the system — the API, the playback layer, the admin console, “all user-facing endpoints”.
2. Quality attribute. Latency, availability, encryption, accessibility — mapped to one ISO/IEC 25010 characteristic.
3. Metric. What you’re measuring (p95 ms, monthly uptime%, WCAG level).
4. Threshold. The number, with a unit.
5. Condition. The load, region, or scenario in which the threshold must hold (“at 1k RPS, 95% from EU regions”).
6. Verification method. How you’ll prove it — load test, audit, monitoring, manual screen-reader pass.
Bad: “The system shall be fast and secure.”
Good: “The /search endpoint shall return p95 <400 ms at 800 RPS sustained from EU regions, with all responses served over TLS 1.3, verified by a k6 load test in CI on every release and a quarterly external pentest.”
A reusable NFR template
NFR-ID:        PERF-API-001
Subject:       Public REST API
Attribute:     Performance efficiency / time behaviour
Metric:        p95 latency
Threshold:     <500 ms
Condition:     1,000 RPS sustained, 70/30 read/write, EU+US traffic
Verification:  k6 nightly load test, dashboards in Grafana
Owner:         Platform team (lead: @eng-lead)
Review cadence: Quarterly
Want a template you can paste into your spec today?
We’ll send you the Fora Soft NFR template and walk through your top three risk areas in a 30-min call.
The cost of nines — what each uptime tier really buys you
Buyers love nines. Architects know each one roughly multiplies cost. Pick the lowest tier you can defend — and revisit it as you scale.
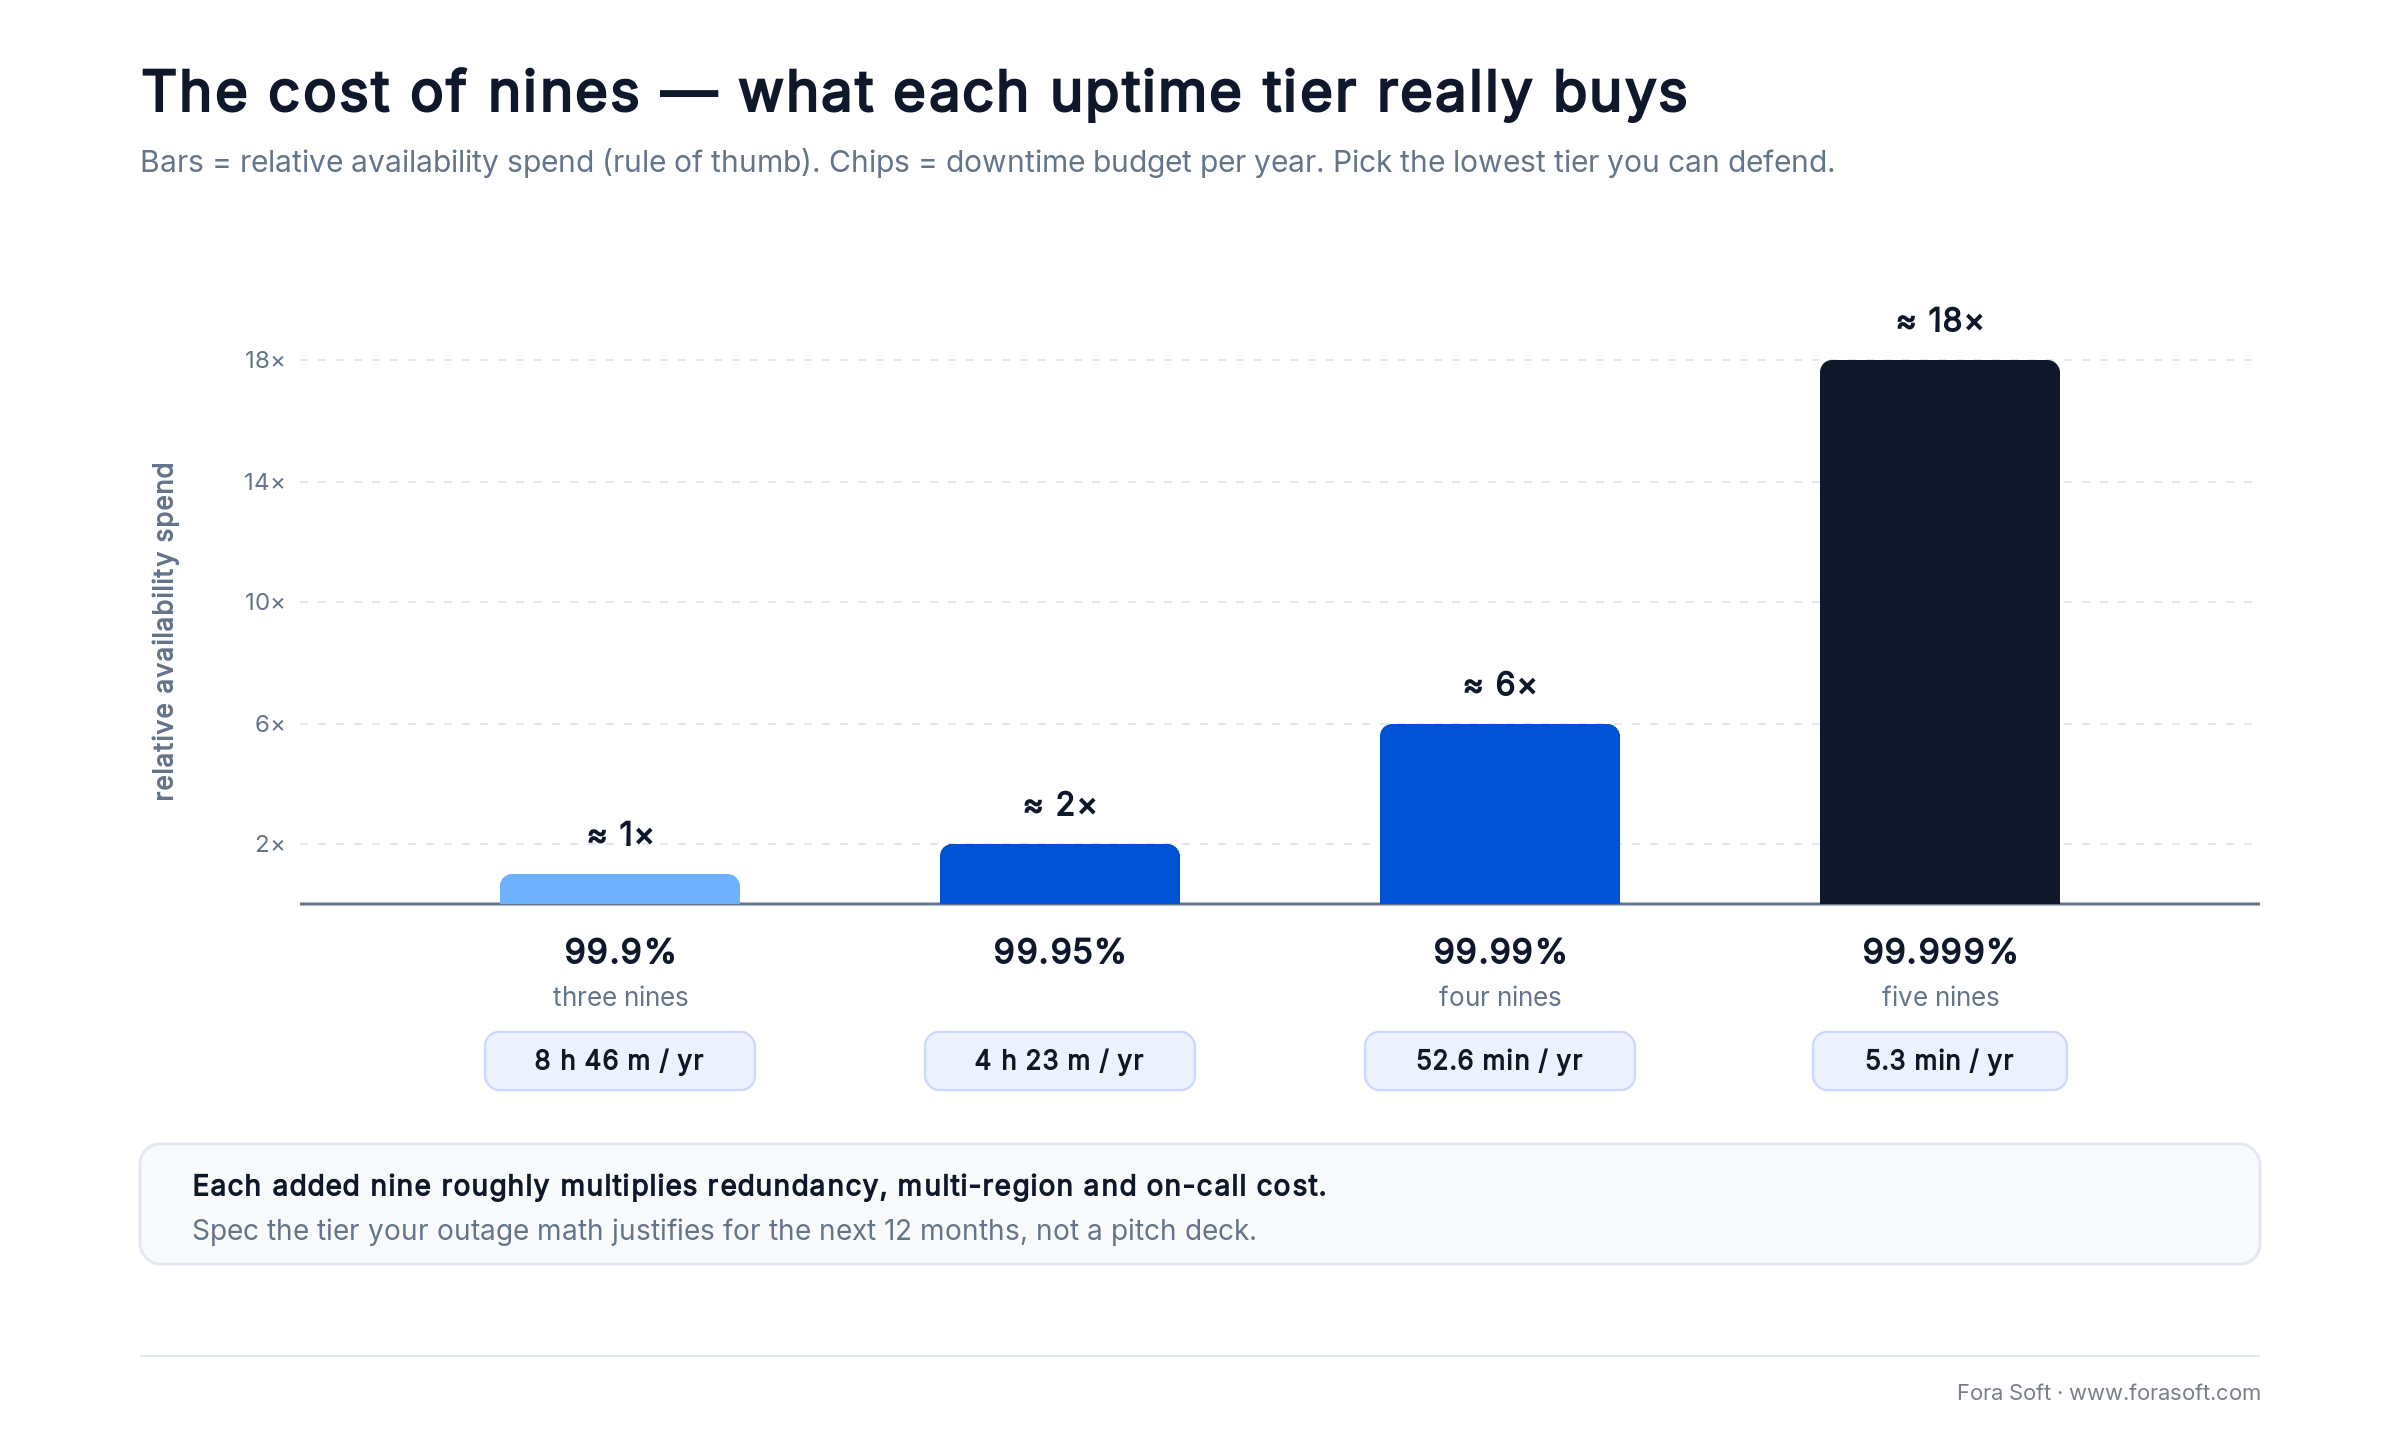
Figure 4. Each added nine multiplies the availability bill. The chips show the yearly downtime budget each tier buys.
| SLO | Allowed downtime / month | Allowed downtime / year | What it implies |
|---|---|---|---|
| 99.0% | ~7.2 h | ~3.65 d | Single region, business-hours on-call. Fine for early MVPs and internal tools. |
| 99.5% | ~3.6 h | ~1.8 d | Single region, automated failover within services. Common SaaS starting point. |
| 99.9% (“three nines”) | ~43 min | ~8.76 h | Multi-AZ, 24/7 on-call, mature observability. Default for paid B2B SaaS. |
| 99.95% | ~21.6 min | ~4.38 h | Multi-region active/passive, blue-green deploys, chaos drills. Enterprise SLAs. |
| 99.99% (“four nines”) | ~4.3 min | ~52.6 min | Multi-region active/active, automated regional failover, error budgets enforced. |
| 99.999% (“five nines”) | ~26 s | ~5.26 min | Telco / fintech core; rarely justified for SaaS. Costs explode. |
Reach for 99.9% when: you have paying B2B users with contractual SLAs, you can afford 24/7 on-call, and a 43-minute monthly outage doesn’t kill renewals. Going higher should follow customer demand and revenue, not engineering pride.
Compliance, mapped to NFRs (GDPR, HIPAA, PCI, SOC 2, EU AI Act)
Each framework looks like a legal document and lands in your repo as a list of NFRs. The shortlist below covers what we see in 2026 procurement.
GDPR (EU)
Encryption at rest and in transit; data minimisation; data residency in the EU for personal data when contracted; data subject requests answered within one month, extendable by two further months for complex cases (GDPR Art. 12(3)); erasure without undue delay; breach notification to the DPA within 72 hours; documented DPIAs for high-risk processing.
HIPAA (US healthcare)
PHI encrypted (AES-256 at rest, TLS 1.2+ in transit); RBAC with least-privilege; immutable audit logs retained 6+ years; signed BAAs with every sub-processor; breach notification to affected individuals without unreasonable delay and no later than 60 days. Hosting on a HIPAA-eligible provider (AWS, GCP, Azure healthcare-eligible services). Note the moving target: a 2025 HHS Security Rule proposal (NPRM) would make encryption and MFA mandatory rather than today’s “addressable” — still not final as of October 2026: OCR missed its May 2026 target, and the January 2025 proposal remains the text to design against. We build HIPAA-grade telemedicine and design MyOnCallDoc against this baseline.
PCI DSS v4.0.1
v4.0.1 is the current version, and its future-dated requirements became mandatory on 31 March 2025 (usd AG, 2025). Don’t store PAN if you can avoid it — tokenise via Stripe, Adyen, Braintree. If you must, network segmentation, quarterly ASV scans, annual pentest, MFA on cardholder-data-environment access. Most product teams should aim to be SAQ-A or SAQ-A-EP, not full PCI Level 1.
SOC 2 Type II
Five Trust Service Criteria (security mandatory; availability, confidentiality, processing integrity, privacy optional). Type II requires evidence of controls operating over 6–12 months. Implies vendor management, change-management, access-review, incident-response policies — expressed as NFRs in product backlog (e.g., “Production access reviewed quarterly, evidence in Vanta”).
Reach for SOC 2 Type II when: enterprise sales is your primary growth channel and 50%+ of pipeline asks for the report. Skip it (or defer to Type I) for the first 18 months if your customers are SMB and the audit cost — typically $25k–75k/year — would meaningfully extend your runway.
EU AI Act (transparency live 2 Aug 2026)
The dates matter. Article 50 transparency obligations (label AI chat, mark AI-generated content) apply from 2 August 2026, with fines up to €15M or 3% of global turnover; high-risk (Annex III) obligations were deferred to 2 December 2027 and AI inside regulated products (Annex I) to 2 August 2028 by the Digital Omnibus on AI, adopted in June 2026. Systems already on the market before 2 August 2026 get until 2 December 2026 for machine-readable marking of AI-generated content. If your product uses AI in high-risk categories (HR, education, biometrics, critical infrastructure, justice), you owe risk assessments, training-data documentation, human oversight, accuracy, resilience and cybersecurity reporting, and post-market monitoring. Bake these into NFRs early — retrofitting is expensive. If video or audio is involved, our AI for video engineering guide shows where these controls land.
EU Cyber Resilience Act (reporting live 11 Sep 2026)
Any product with digital elements sold in the EU falls under the CRA. Since 11 September 2026, manufacturers must report actively exploited vulnerabilities and severe incidents: early warning within 24 hours, notification within 72 hours, final report within 14 days of a fix (European Commission). The full security requirements apply from 11 December 2027. As NFRs: an SBOM per release, a vulnerability intake channel, a documented support period with security updates, and an on-call path that can meet a 24-hour clock.
EU Data Act (cloud switching since 12 Sep 2025)
The Data Act has applied since 12 September 2025. For SaaS and cloud products it turns exit into a requirement: customers must be able to switch provider and export their data, and switching charges disappear completely from 12 January 2027. Write it as a flexibility NFR: full export in documented, machine-readable formats, and a tested exit runbook.
ISO/IEC 27001:2022
An information security management system, not a product checklist — but its Annex A controls (93 in the 2022 revision) translate into concrete NFRs: change management, asset inventory, vulnerability management, business continuity.
A real NFR spec for a video communication platform
Below is the kind of NFR list we hand to engineering when we kick off a video product — trimmed for readability. Use it as a starting template, not a religion.
| ID | Requirement | Verification |
|---|---|---|
| PERF-01 | Glass-to-glass video latency <300 ms p95 within the same region (EU–EU, US–US). | Synthetic call probes every 5 min, geographically distributed. |
| SCAL-01 | Single SFU instance handles 1,500 publisher + subscriber tracks at 720p 30 fps. | Quarterly load test using synthetic peers. |
| AVAIL-01 | 99.9% monthly uptime for signalling and media plane, excluding scheduled maintenance windows. | Public status page with synthetic checks. |
| SEC-01 | All media transported over DTLS-SRTP. End-to-end encryption (Insertable Streams) optional per room. | Code review + WireShark capture in QA. |
| SEC-02 | Tokens are short-lived (max 1 h) and bound to a single room. | JWT inspection in tests; pentest. |
| COMP-01 | Recordings storage HIPAA-eligible (KMS-encrypted, BAA-covered bucket). | Vendor BAA on file; bucket policy review. |
| USAB-01 | UI conforms to WCAG 2.2 AA; captions available on all calls when STT is enabled. | axe + manual screen-reader. |
| RECOV-01 | RTO 30 min for signalling; RPO 5 min for chat history. | Quarterly DR drill. |
| COST-01 | Cost per concurrent video minute ≤ $0.0005 at 70% utilisation. | FinOps dashboard, monthly review. |
For a real-time video build like TransLinguist or a high-traffic e-learning platform like BrainCert, the same skeleton expands to 60–100 line items.
MVP vs scale-up vs enterprise — spec for the stage you’re in
Spec the NFRs you can pay for — and architect so you can tighten them later without a rewrite. More on MVP scoping here.
| Stage | Performance | Availability | Security | Compliance |
|---|---|---|---|---|
| MVP (0–1k users) | p95 <1.5 s | 99.0–99.5% | HTTPS, basic auth, secrets in vault | Privacy policy, GDPR basics |
| Scale-up (1k–100k) | p95 <500 ms | 99.9% | MFA, RBAC, audit logs, SCA in CI | SOC 2 Type I → II within 12 mo |
| Enterprise (100k+) | p95 <300 ms, multi-region | 99.95–99.99% | Pentest, key rotation, vuln SLA, BYOK | SOC 2 II + ISO 27001 + sectoral (HIPAA / PCI) |
Mini case — how a tightened NFR list saved a Fora Soft client a quarter of rework
A mid-market healthcare client came to us with a partly-built telemedicine product. Functional spec was thorough — appointments, video visits, e-prescriptions. NFR section was four bullets: “HIPAA, fast, 99.9%, mobile-friendly.” Three weeks before pilot, their pentester flagged that audit logs were stored alongside PHI in the same Postgres, with no segregation, no immutability and 90-day retention.
We re-wrote the NFRs first, build plan second. Twelve weeks: split logs into a write-once store, added KMS-CMK encryption with rotation, set RTO/RPO to 30 min/5 min, formalised the BAA chain, and rebuilt the load profile against a defended 99.9% SLO. Pilot launched on schedule with HIPAA-acceptable evidence. The pentest took eight days instead of an estimated five weeks because every control had a written, testable NFR behind it.
The lesson isn’t “hire Fora Soft.” It’s that the cost of writing the NFRs properly was about 1% of the cost of fixing them under a deadline.
A decision framework — choose your NFRs in five questions
Q1. What does your worst customer outage cost in dollars per hour? If it’s <$1k, 99.9% is fine. If it’s $50k+, you’re paying for 99.95% whether you spec it or not.
Q2. What regulation, if any, will be applied to your product in the next 18 months? Don’t guess — ask sales which deals are blocked on SOC 2 / HIPAA / FedRAMP. That’s your answer.
Q3. What is your realistic peak load 12 months from now? Multiply current peak by 3×. If that breaks your stack, you have an NFR gap. If it’s 30×, re-architect now — you can’t scale into it.
Q4. Where do your users physically sit? EU-only means data residency; global means CDN, regional latency targets, time-zone-aware ops. Don’t inherit Silicon Valley assumptions.
Q5. Who will run this in two years? If it’s a different team, prioritise maintainability and observability NFRs hard. If it’s you, you can defer some doc requirements but still log everything.
Five pitfalls we see in real NFR specs
1. “Fast,” “secure,” “scalable” with no number. If a vendor accepts those words, they’ll deliver whatever’s easy. The spec is the only place to win this argument.
2. NFRs without owners. “Performance” without a name on it ends up nobody’s problem. Tag every NFR to a team and a person.
3. Compliance treated as a sticker. “HIPAA-compliant” on a marketing page is not a control. The control is “PHI encrypted with customer-managed keys, audit logs immutable for 6 years, BAAs on file with every sub-processor.”
4. Over-spec for the current stage. Demanding 99.99% uptime for a 200-user MVP burns runway you need for product–market fit. Spec what your contracts demand plus a small headroom; revisit quarterly.
5. NFRs disconnected from monitoring. If you spec a p95 latency, the dashboard for it must exist on day one of production. Targets without telemetry are wishes.
KPIs to track NFR health in production
Quality KPIs. p95 / p99 latency per critical path; error rate (4xx, 5xx, dropped media frames); accessibility scan score; mean test coverage. Thresholds: latency within budget >95% of measurement windows; error rate <0.5% on production traffic.
Reliability KPIs. Monthly uptime vs SLO; error budget burn rate; MTTD / MTTA / MTTR; failed DR drills count. Thresholds: error budget burn <100% of monthly budget; MTTA <5 min; zero failed DR drills per year.
Business KPIs tied to NFRs. Conversion impact of latency (every 100 ms of added p95 latency on key user paths costs measurable conversion — track it); SLA credits paid; security incidents and time-to-resolve; compliance audit findings count and severity.
Inheriting a system without an NFR spec?
We do fixed-scope code & architecture audits for new clients — written report, NFR gap list, prioritised fix plan inside two weeks.
When you should not write a 60-page NFR document
A pre-launch validation prototype, a one-month trade-show demo, an internal tool used by 12 people — these don’t need the full ISO/IEC 25010 treatment. Two pages of NFRs (“HTTPS only, no PII stored, can be deployed to a single ECS task, accessibility deferred”) is plenty. Optimise for shipping, not for procurement.
The trigger to upgrade is the first paying customer who asks for a security questionnaire. That afternoon, you write a real NFR document.
Using NFRs to choose a software development partner
If you’re evaluating outsourced engineering or augmenting your team — whether a dedicated development team or a fixed-scope build — NFR fluency is the cleanest filter we know.
Five questions to ask candidates. Have them walk you through (1) the NFR taxonomy they use; (2) one production system with its real SLOs and how they were chosen; (3) a war story where an NFR was missed and what changed; (4) how they hand-off NFRs from spec to monitoring; (5) what they refuse to over-promise. The vendors who can’t answer (3) honestly are the ones who’ll surprise you in month four. Our hiring bar for engineers exists precisely so we can answer (3) honestly.
A useful test: ask the candidate to review your current product against your NFR list and write down the gaps. A short written verdict is a small commitment that surfaces the architectural truth, and it is what our independent architecture review delivers: what to keep, what to change and why. For the budget side, our estimation playbook is here.
FAQ
What are non-functional requirements in plain English?
They are the quality rules around your features — how fast, how reliable, how safe, how accessible, how scalable, how compliant the product must be. Functional requirements describe behaviour; NFRs describe how well that behaviour must work.
How many non-functional requirements should an MVP have?
For a focused MVP, 15–25 NFRs covering the essentials — a single uptime target, p95 latency, encryption baseline, basic accessibility, browsers/devices supported, GDPR fundamentals if you serve EU users, and a simple recoverability plan. Add specificity in the next stage rather than over-spec on day one.
What is the difference between an SLO, an SLA and an NFR?
An NFR is the engineering target (“p95 latency <500 ms”). An SLO is the internal promise based on it (“p95 latency <500 ms in 99% of monthly windows”). An SLA is the contractual promise to a customer with consequences (service credits) when missed. NFRs feed SLOs feed SLAs.
Are non-functional requirements the same as quality attributes?
In modern usage, yes — the ISO/IEC 25010 standard explicitly frames quality attributes (performance efficiency, reliability, security, etc.) as the canonical NFR taxonomy. Older texts also use “ilities” for the same idea (scalability, observability, maintainability).
Who should write the NFRs — product, engineering, or both?
Both. Product owns the business intent (“our SLA must be 99.9% to win enterprise deals”); engineering translates that into achievable, testable thresholds and flags trade-offs. Without both, you get either dreamy targets nobody can hit or pragmatic targets that lose deals.
Can non-functional requirements change over time?
They should. Review NFRs quarterly — tighten what your traffic now demands, relax what was over-spec, add new categories as you enter new markets (e.g., adding HIPAA when you sign your first US healthcare customer). NFRs are living, like the product.
What does NFR mean?
In software and IT, NFR means non-functional requirement: a rule for how well a system works, such as p95 latency, uptime, encryption or accessibility. In licensing, NFR means “not for resale”.
What is an NFR environment?
A production-like environment reserved for non-functional testing: load, soak, failover and security tests. It needs production-sized data and infrastructure, otherwise the results do not predict production.
Which ISO standard defines non-functional requirements?
ISO/IEC 25010:2023 is the product quality model: nine characteristics that every NFR maps to, with scalability filed under flexibility. ISO/IEC/IEEE 29148 covers how requirements are written and managed.
How do I verify a vendor is meeting its NFRs?
Insist on three artefacts: a public status / SLA page, a quarterly performance & security report (real measurements, not marketing), and the right to periodic third-party pentest or audit. Without all three, you’re trusting the sales team.
What happens when functional and non-functional requirements conflict?
They will. End-to-end encryption fights server-side search; offline-first fights real-time consistency. Resolve in the spec, not in production: either drop the conflicting feature, accept a softer NFR, or invest in the architecture (e.g., client-side search index) that lets you have both. Document the trade-off so the next team knows why.
What to Read Next
Estimation
A guide to estimating software development projects
How we turn an NFR list into a defensible budget and timeline.
MVP
What an MVP is and what to cut from it
The companion piece on functional scope — how much is too much for v1.
Code audit
How to run a code & architecture audit
Use this when an inherited codebase has no NFR spec at all.
Hosting
AWS vs DigitalOcean vs Hetzner — which fits your NFRs
A frank comparison once you know your latency, residency and cost numbers.
Security
WebRTC security in plain language
The exact security NFRs you need for any real-time video product.
Ready to turn your NFR list into a real engineering plan?
Non-functional requirements are the quietest determinant of whether your product gets reviewed, renewed and recommended. Spec them with numbers, owners and verification — mapped to ISO/IEC 25010 — and treat them as living. Tighten as paying customers demand it; soften when you’re burning cash on perfection nobody asked for.
If you want a partner that takes NFRs seriously from week one — not as a procurement form to fill in at the end — that’s the bar Fora Soft has held for 21 years. Bring us a draft, an inherited mess, or just a hypothesis. We’ll tell you what’s realistic, what’s missing, and what we’d build first.

The handbook · 7 volumes
Fora Soft Video Engineering Handbook
A latency target or an uptime tier in an NFR spec is only as good as the team's understanding of what sits beneath it. We wrote a seven-volume handbook on the full video stack, from encoding and delivery to sound and AI. For a video communication platform, start with the volume on WebRTC, CDNs and QoE, then the latency budget volume and the AI volume on compliance and the EU AI Act. Written by Nikolay Sapunov, CEO at Fora Soft.
Browse the handbook on Amazon →7 volumes · 9,000+ pages · Kindle & paperback
Let’s pressure-test your non-functional requirements together
30 minutes with a Fora Soft architect — bring your draft, leave with a prioritised gap list and a realistic cost envelope.

